Inside Penzzer
From CAN bus campaigns to file-format harnesses to Wi-Fi protocol fuzzing.
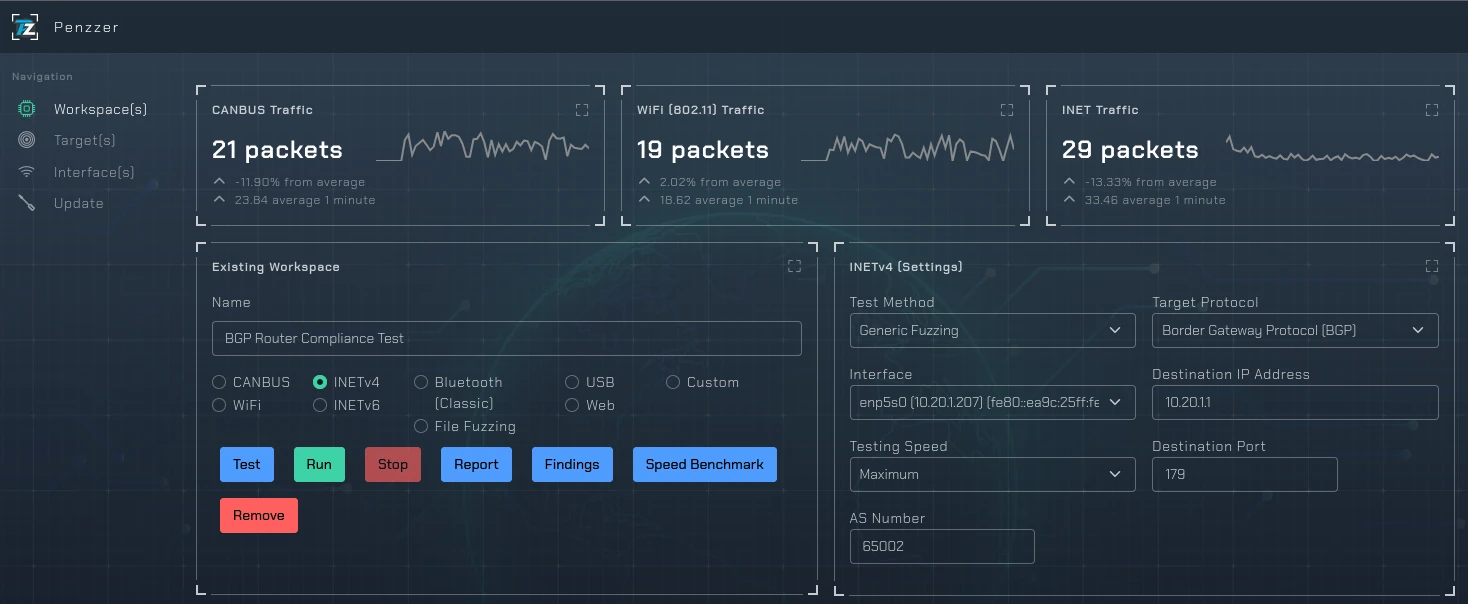
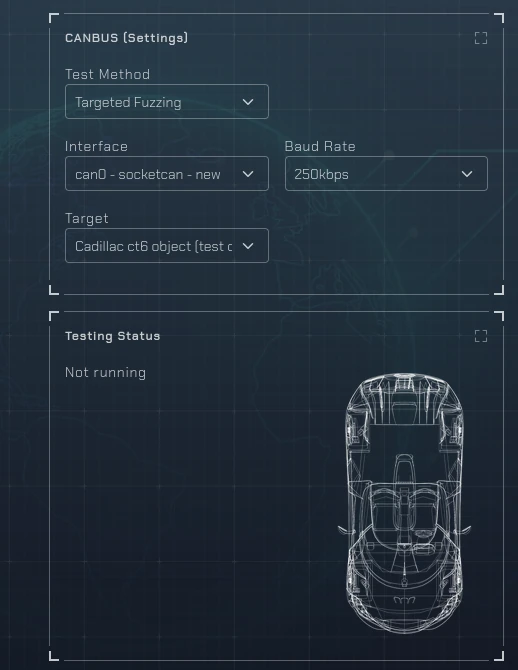
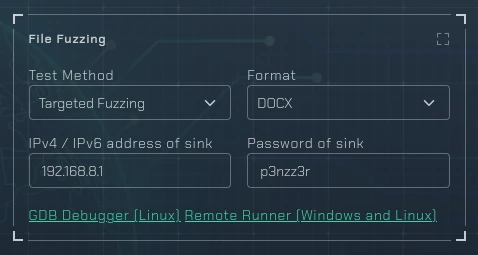
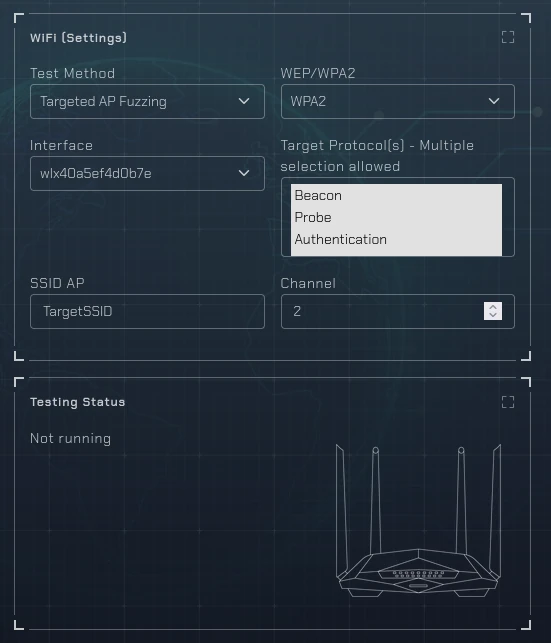
Penzzer is Apona's dynamic fuzz testing platform for medical devices, IoT firmware, and CAN bus / embedded targets. It drives real inputs into running systems to find the crashes, memory faults, and logic flaws static analysis cannot reach.
Static analysis reasons about code. Penzzer attacks behavior: the running protocol, the firmware on the device, the message on the bus.
Drives malformed and adversarial inputs into connected medical devices and their protocols. Surfaces safety-critical crashes, memory faults, and parsing bugs before they reach a patient.
Exercises firmware across ARM, MIPS, and other embedded architectures to find memory-safety and parsing bugs before shipping.
Generates and mutates bus traffic against ECUs and embedded controllers. Built for automotive and industrial targets.
From CAN bus campaigns to file-format harnesses to Wi-Fi protocol fuzzing.
Scoped POCs on real targets: your firmware image, your CAN-bus harness, your medical-device prototype. We bring the fuzzing setup and an engineer; you bring the target. The output of the POC is a list of bugs and a defensible coverage report.
Penzzer is a strong service-line addition for AppSec firms, embedded-security consultancies, and medical or automotive security boutiques. The Apona channel program covers deal registration, technical enablement, and POC co-delivery. See /partners.
"I found Penzzer incredibly effective in identifying vulnerabilities and enhancing the security of our automotive components. Its user-friendly interface, customization options, and exceptional support make it an indispensable asset for efficient and comprehensive security testing."
Tell us the target you are trying to fuzz. We will route to Roger for technical conversations or Aviram for channel ones.