Four products, one channel
Different buyers, different targets, one partner program. Pick the surface you defend.
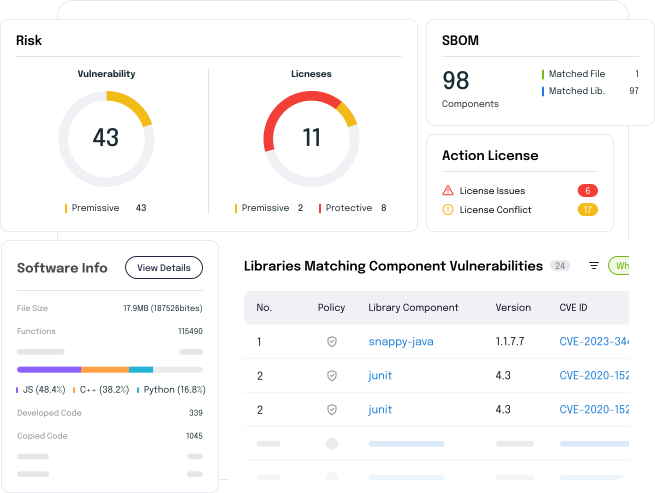
SAST, SCA, and supply-chain security. Find vulnerabilities and license issues, generate SBOMs, and keep the triage queue from drowning the team.
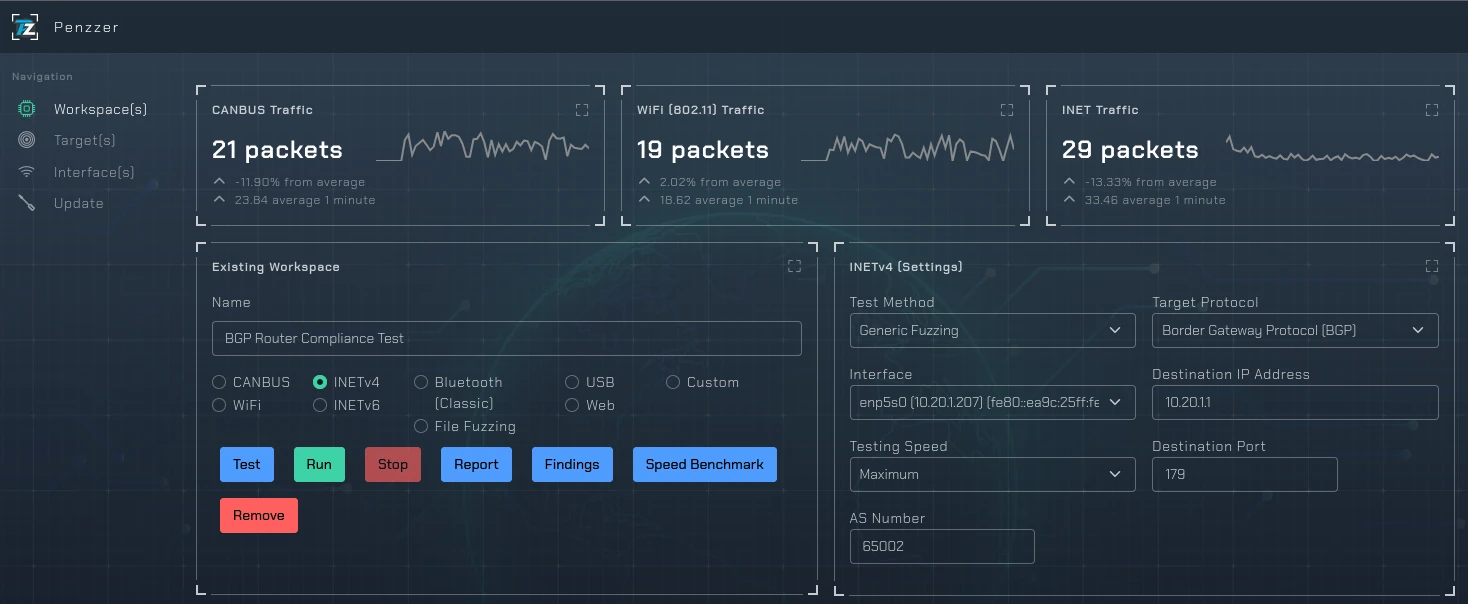
Dynamic fuzzing for medical devices, IoT firmware, and CAN bus / embedded targets. Finds the runtime crashes and memory faults static analysis cannot reach.
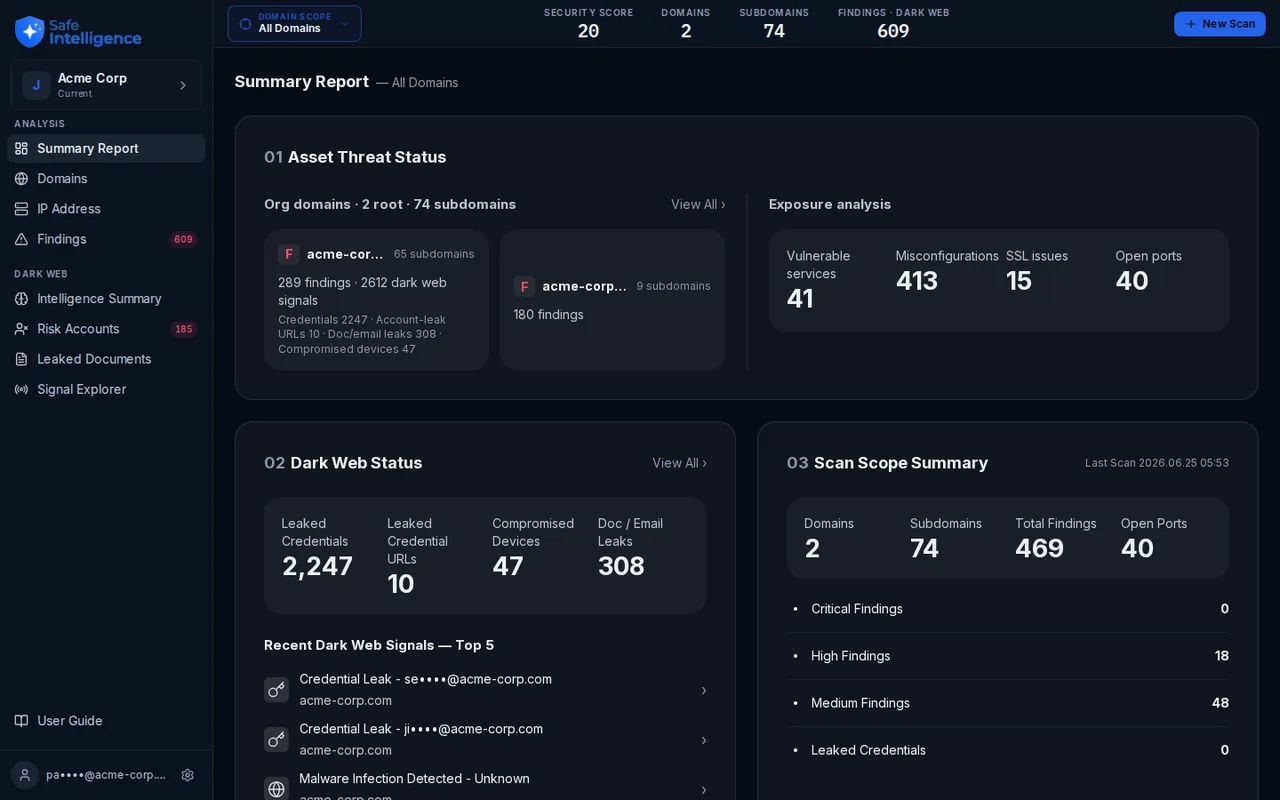
Agentless EASM and dark-web credential monitoring for SMBs. No agents, no professional services. Sold 100% through the channel - MSPs and MSSPs add it as a managed service in hours.
One vault for the credentials a team shares, with per-user permissions so people get access rather than passwords. Audit trails, expiration policies, and dark-web monitoring for exposed credentials.