Find, fix, and comply
From SBOM generation through vulnerability remediation to regulator-ready reporting.
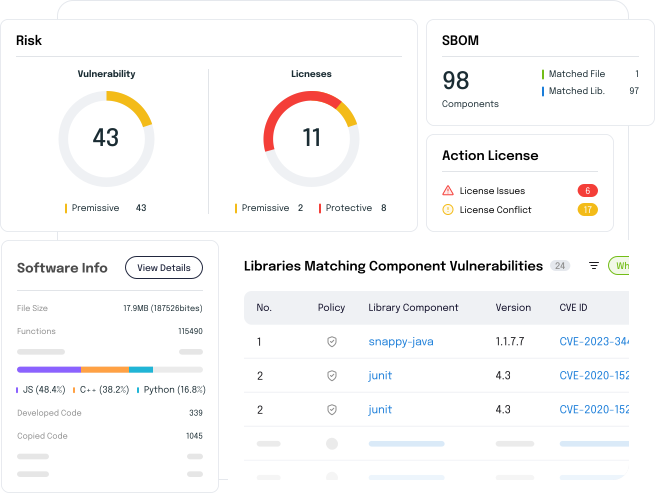
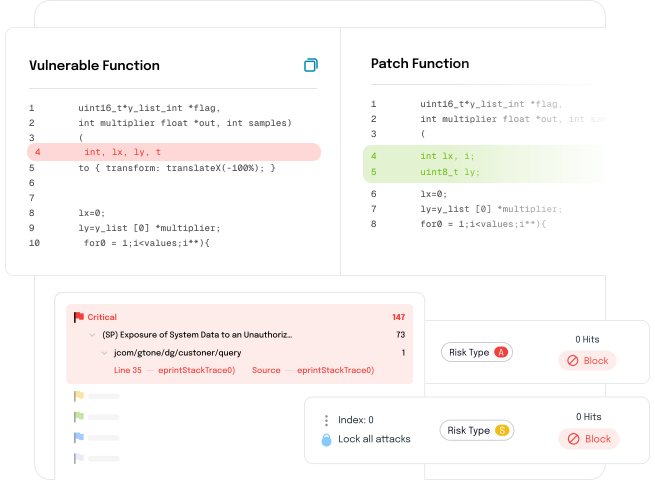
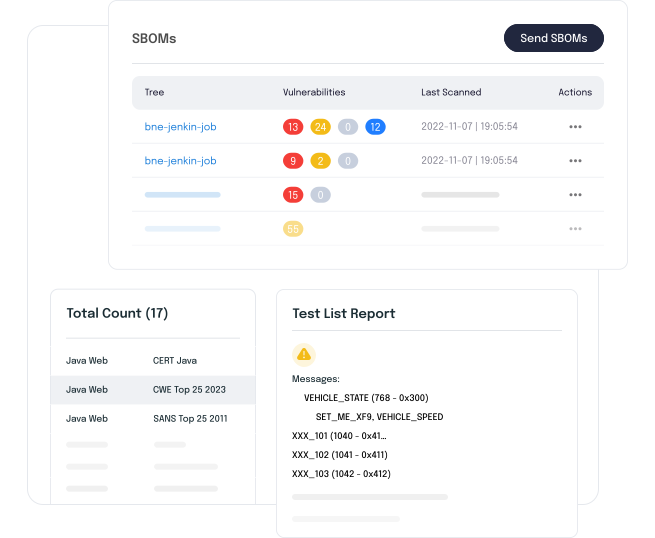
Labrador is Apona's SAST, SCA, and supply-chain security platform. Built for AppSec teams that care about signal-to-noise, and tuneable enough that the triage queue stops being a graveyard.
Static analysis of proprietary source code against a tuneable rule set. The pitch is keeping the triage queue from drowning the team. Rule sets are tuned per stack, not shipped as one global default.
Vulnerability and license detection across open-source and third-party dependencies, including transitive paths and reachability hints so the team can prioritise what is actually exploitable.
SBOM generation in standard formats (CycloneDX, SPDX) and supply-chain controls for what enters a build. The post-XZ baseline most security teams now have to defend.
From SBOM generation through vulnerability remediation to regulator-ready reporting.
Scoped POCs on your codebase with a real Solutions Engineer in the room. We tune rule sets to your stack so the false-positive rate stays in human range. Conversation first, demo second, procurement when it is actually time.
A channel program for Labrador with deal registration, joint POC support, technical enablement for your engineers, and reseller economics designed for service-led firms. See /partners.
"We were looking for a solution that could check a lot of boxes: code review and vulnerability scanning (including OSS), vendor risk and compliance management, integration with our CI/CD and monitoring tools, comprehensive patch recommendations, and IRP testing. Apona checks all of these boxes, without slowing us down."
"Almost immediately after adding Apona's SAST and SCA tools into our pipelines, we were able to see enhancements to our security features. We were able to find and fix software vulnerabilities, licensing issues, and even conduct compliance audits without needing to hire more engineers."
"There are a lot of SCAs out there, and many are great. We chose Apona because it goes deeper into the source code and even provides function-level fixes."
"Apona was able to quickly generate SBOMs and import them into our SBOM management tool so we could find any issues before they make it into our medical devices. Their vulnerability detection rate, patch recommendations, and code-level modifications have been phenomenal."
Tell us what you are trying to do. We will route this to Roger for technical conversations or Aviram for channel ones, whichever fits.